


Algorithmic Pricing and Antitrust Risk: A New Oversight Duty for Boards

There used to be a fairly easy line a company could reach for: “we didn’t set the price, the software did.” Enforcers have quietly taken that line away. Not understanding what your own pricing tool is actually doing is starting to look less like an excuse and more like the problem itself.
This isn’t a story about artificial intelligence getting smarter. It’s a story about governance catching up to a risk that’s been sitting inside ordinary pricing software for a while now, mostly unexamined.
Executive Summary
For a board, algorithmic pricing risk boils down to one question dressed up in technical language: is this pricing tool behaving like normal business software, or is it quietly doing the work that direct coordination between competitors used to do? Regulators spent 2025 and 2026 answering that question with real teeth. California rewrote its core antitrust statute, the Cartwright Act, in October 2025 to explicitly outlaw using or distributing a shared pricing algorithm as part of an arrangement that restrains trade. The FTC launched a rulemaking process in April 2026 aimed at pricing transparency and personalised pricing. DOJ officials said in June 2026 that criminal prosecution for algorithmic collusion is still very much on the table. And more than 40 state-level surveillance pricing bills are moving through legislatures right now, across more than twenty states. None of that reads like a niche legal footnote anymore. It reads like an enforcement priority — and one that’s arrived faster than most boards’ oversight structures have caught up to.
Quick Answers
What is algorithmic pricing, and why does it create antitrust exposure?
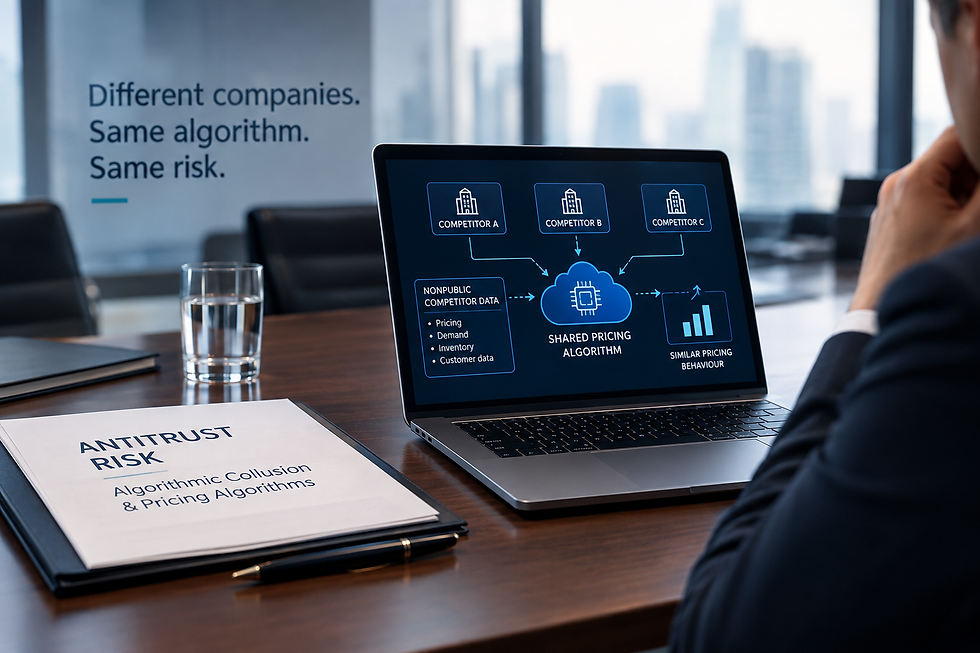
It’s software that sets or recommends prices based on data — demand, cost, competitor behaviour, sometimes individual customer signals. The antitrust problem shows up when competitors share the same algorithm, particularly one fed with each other’s nonpublic pricing data, in a way that functions like coordinated pricing rather than independent competition.
Is it illegal to use a pricing algorithm?
On its own, no. Algorithmic and dynamic pricing are common and generally lawful. The exposure comes from specific circumstances — mainly, a shared tool across competing firms that pools nonpublic competitor data, which can substitute for direct price-fixing even without anyone actually talking to a rival.
How is that different from ordinary price-fixing?
Ordinary algorithmic pricing reacts to public signals — your own costs, visible market demand, publicly posted competitor prices. It tips into price-fixing territory once a shared tool pools nonpublic data from multiple competitors and uses it to nudge their prices toward each other.
Can boards actually be held responsible for what a pricing algorithm does?
Liability generally attaches to the company itself, but courts and regulators are leaning toward a standard where firms should reasonably have known what their pricing tools were doing. That shifts the absence of board-level oversight from a footnote into something that actually matters when enforcement risk gets assessed.
Why This Landed on the Board’s Desk, Not Just Legal’s
Dynamic pricing isn’t new. Airlines have priced by demand for as long as most people reading this have been flying. What’s changed is the mechanism underneath it, and specifically the data. Once a pricing algorithm gets licensed from a shared vendor, and that vendor is quietly feeding it nonpublic pricing or occupancy figures pulled from several competing clients, the tool can end up doing something that looks a lot like what antitrust law has banned for decades — coordination — minus the part where anyone actually picked up a phone.
RealPage is the case most people in this space already know. The rental-pricing software vendor, along with property manager Greystar, reached proposed settlements with federal enforcers in 2025 tied to allegations around algorithmic rent-setting, following a wave of related state litigation. Those settlements, still pending court approval, are functioning as an informal road map across the industry for what regulators will and won’t accept going forward.
It’s worth being fair to the other side of the ledger too, though, because the law isn’t blanket. In Gibson v. Cendyn Group, the Ninth Circuit found that competing Las Vegas hotels using pricing software from the same vendor hadn’t violated antitrust law — not on those facts, anyway. The court’s reasoning came down to evidence: nothing showed the arrangement actually pooled nonpublic competitor data in a way that enabled coordination. A related case, Mach v. Yardi Systems, landed on similar ground — summary judgment for the defendants, because the software wasn’t shown to combine nonpublic competitor pricing to suggest rates.
Put those cases side by side and a genuinely useful line appears. The legal risk was never “using pricing software.” It’s whether that software is functioning, quietly, as a pipe for competitor data to flow between rivals. That’s a distinction with enough nuance that no board should assume a vendor contract nobody’s actually read has already handled it.
What Oversight Actually Looks Like
Risk or audit committees need to start putting the same pointed questions to pricing and revenue teams that they’d already put to, say, a major cloud vendor or a critical cybersecurity partner. Which third-party pricing tools does the business actually run? What data trains or feeds each one — and is any of it nonpublic competitor information, even by an indirect route? Has legal genuinely reviewed how the vendor’s software works, or has that review just been assumed because the vendor seems reputable?
The stakes here are higher than they look at first glance. Courts increasingly ask whether a company should have understood its own pricing tool’s mechanics, regardless of whether anyone intended to collude. That’s a meaningfully tougher standard than “we never personally agreed to fix prices.” Responsibility for closing that knowledge gap runs upward, to governance — not downward to whichever analyst happened to configure the system two years ago.
A Working Framework for Boards
A short list of concrete steps maps closely onto what regulators are already telling companies to do.
Build an actual inventory. Know which pricing tools exist across the business, and whose data trains each one. Sounds obvious. Routinely doesn’t happen, particularly in larger companies where different divisions adopt pricing software independently, with no central visibility into any of it.
Test before and after deployment. Regulators have been explicit that dynamic pricing tools should be tested both prior to launch and on an ongoing basis, specifically to catch bias, discriminatory outcomes, or collusive potential while it’s still a fixable problem rather than a live legal one.
Review the vendor relationship properly. If a pricing tool comes from a third party, someone with actual authority — not the sales deck — needs to understand what data other clients feed into the same system, and whether any of it crosses into sharing nonpublic information with your own competitors.
Track the regulatory landscape actively. This can’t be a once-a-year compliance box. More than 40 surveillance pricing bills and close to 30 digital shelf label bills were moving through more than twenty state legislatures as of mid-2026, layered on top of federal rulemaking from the FTC. A framework built once and forgotten will be stale within a single legislative session.
A Real-World Example
RealPage and Gibson v. Cendyn sit right next to each other as a useful before-and-after. RealPage faced enforcement tied to claims that its software pulled in nonpublic rental data across multiple landlords to shape pricing recommendations — precisely the kind of data pooling regulators treat as a stand-in for illegal coordination. Cendyn’s hotel pricing software survived appellate scrutiny specifically because the record didn’t show that same kind of nonpublic data commingling. Same broad category — shared vendor pricing software across direct competitors — genuinely different legal outcomes, and the difference came down almost entirely to what the software did with competitor data behind the scenes. That’s exactly the level of detail a board’s oversight process needs to be able to reach, not delegate away entirely.
FAQs
Does this only affect certain industries?
Enforcement so far has clustered in rental housing, hospitality, and consumer retail and delivery, but any company using shared or third-party pricing tools carries some exposure. The underlying legal principle — nonpublic data pooling functioning as coordination — isn’t industry-bound.
Is “surveillance pricing” the same issue as algorithmic collusion?
Related, not identical. Surveillance pricing usually refers to setting individualised prices off personal data — location, browsing history, purchase patterns — and sits closer to consumer protection and privacy law. Algorithmic collusion is a competition-law concern about pricing tools coordinating across competitors. Some 2026 state laws, Connecticut’s among them, fold both concerns into a single statute, which adds to the compliance tangle.
Who inside the company should actually own this risk?
Legal, pricing, and the board, together, with real coordination between them. Legal assesses the specific antitrust exposure. Pricing and revenue management run the tools day to day. The board’s job is confirming a genuine link exists between the two — not assuming legal will catch something it was never actually shown.
What’s the one question worth asking first?
Where does this pricing algorithm’s data actually come from. That single question is usually enough to separate ordinary, lawful dynamic pricing from the arrangements regulators are currently building cases around.
Key Insights
“We didn’t know what the algorithm was doing” has gone from a plausible defense to, functionally, part of the violation itself.
The legal line was never about using a pricing algorithm — it’s about whether that algorithm pools nonpublic competitor data, which is exactly what separates the RealPage outcome from the Gibson v. Cendyn outcome.
State-level regulation is fragmenting quickly, which means a compliance review done once is effectively out of date by the time the next legislative session wraps up.
This risk belongs next to other vendor and technology exposures boards already take seriously — cybersecurity, data privacy — not off in some lesser, HR-adjacent category.
Key Takeaways
Boards don’t need antitrust expertise to handle this well. They need to stop treating algorithmic pricing as a detail that lives entirely inside the pricing function and nowhere else. Put one question on the next risk committee agenda: what pricing tools does this company run, whose data feeds them, and has anyone actually confirmed none of that data includes nonpublic competitor information. A company that can answer that cleanly is in a completely different position from one that assumed the vendor already handled it. Given how fast enforcement is moving through 2026, “we assumed” is not a sentence any board wants to be saying out loud when the question finally gets asked directly.
Is Your Board Ready for Algorithmic Pricing Risk?
Algorithmic pricing is becoming more than a technology decision—it is a governance and antitrust issue. Boards need to understand what pricing algorithms use, how they make decisions, and where regulatory exposure may arise.



Comments